

A Data Loss Prevention (DLP) tool can only protect what it manages to understand. This distinction, though simple on the surface, represents one of the greatest challenges in corporate cybersecurity.
Most traditional DLP programs are configured to recognize only highly structured and regulated data, such as credit card numbers (PCI) or national identification numbers (PII). They perform well on what they detect, but leave the majority of the enterprise digital estate completely exposed.
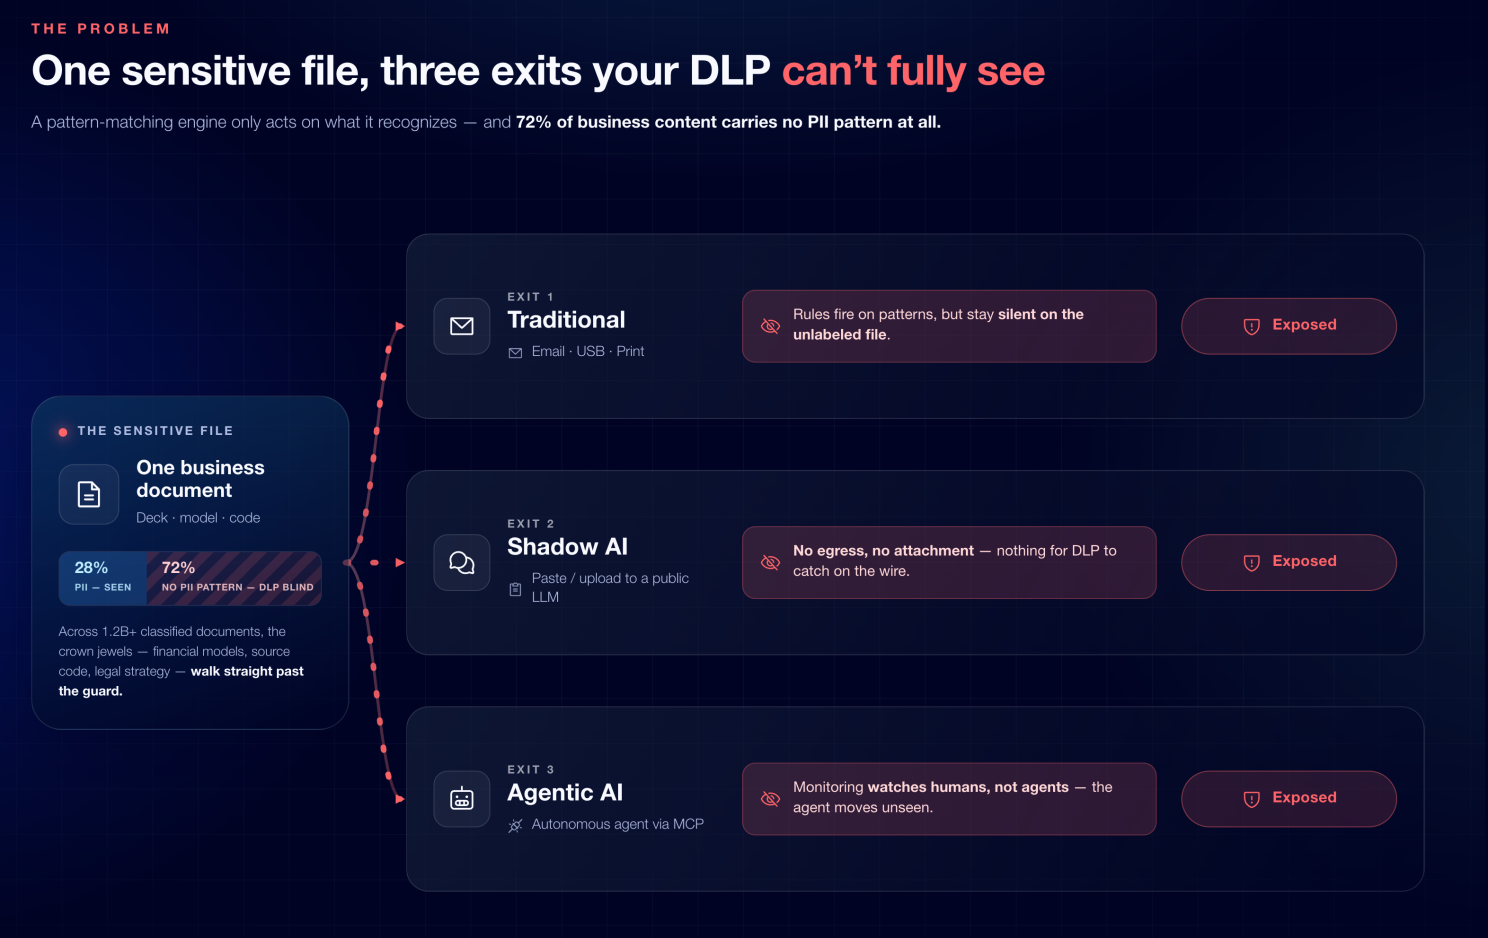
In benchmark analyses conducted by Kriptos across a volume of over 1.2 billion classified documents, approximately 72% of corporate content contains no PII patterns. Yet, that 72% houses the company's strategic intellectual property: financial models, mergers and acquisitions (M&A) material, source code, legal strategies, and price lists. A DLP system will only act on these files if it knows their level of confidentiality in business terms.
To solve this blind spot, Kriptos combines advanced Artificial Intelligence models to maximize accuracy on the 28% containing PII, while custom-tuning those models to each client's corporate taxonomy to identify critical information hidden within the remaining 72%. Since more than 60% of sensitive data is created and resides directly on endpoints (employee laptops), the risk surface expands as AI tools shift to the desktop via local assistants and copilots.
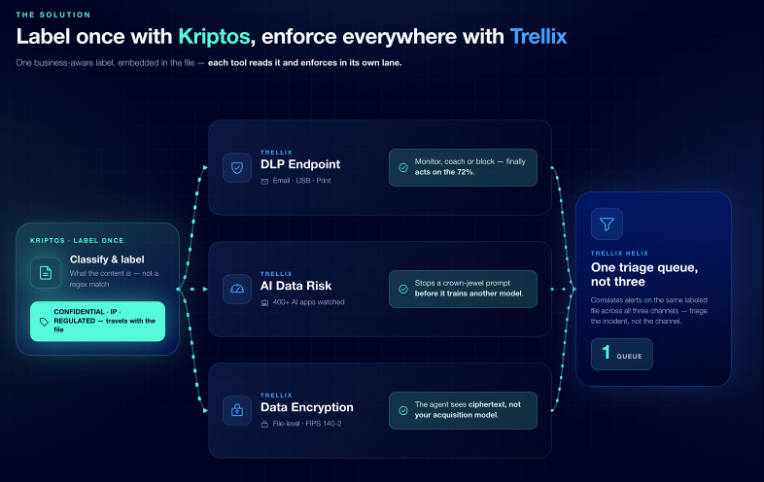
Facing this scenario, the strategic integration between Kriptos and Trellix resolves the visibility gap: Kriptos classifies and labels each file once, embedding business intelligence directly into the document. Trellix then reads that label and executes the appropriate control across every channel.
The Importance of Adapting Data Loss Prevention (DLP) to the AI Era
Traditional cybersecurity was built for a world where data left through email attachments or removable drives. Today, the rapid adoption of generative AI tools and automation through intelligent agents has multiplied exfiltration channels, creating routes that conventional DLP engines cannot monitor natively.
Implementing a modern Data Loss Prevention (DLP) strategy requires shifting from simple rule-based inspection to a contextual data discovery and classification architecture. When classification precedes enforcement, the organization ensures that every operational control responds to the actual value of the asset, aligning security efforts with data compliance and risk management requirements.
The 3 Escape Routes and the Joint Kriptos + Trellix Response
Flow 1
Traditional Exfiltration: Email, USB, and Print
This is the familiar channel for which traditional DLP systems were built. Block rules fire reliably on credit card numbers, but often remain silent on board meeting minutes or strategic presentations that lack labels.
Kriptos solves this flaw by tagging files according to their actual business criticality (regulated, confidential, or intellectual property). Trellix DLP Endpoint reads this label natively and executes the appropriate policy (monitoring, coaching, or blocking) whenever the file attempts to leave via email, removable storage, or printing on managed endpoints.
Flow 2
Shadow AI: Sensitive Prompts to Public LLMs
This is the fastest-growing escape route. An employee copies paragraphs of a confidential contract into a public large language model (LLM) to summarize or clean it up, exposing strategic information without leaving a network download trace.
In this scenario, the Kriptos label feeds the Trellix DLP AI Data Risk Dashboard. The platform monitors sensitive data interactions (clipboard, copy/paste, and file uploads) across a catalog of over 400 AI applications, preventing data leaks before information becomes training material for third-party models.
Flow 3
Autonomous AI Agents: Unauthorized File Access
Autonomous agents connected through protocols like the Model Context Protocol (MCP) are given file access to execute operational tasks. However, an agent with folder access can read any confidential document stored inside it.
To mitigate this risk, Kriptos labels the file as intellectual property or restricted content, and Trellix Data Encryption maintains file-level encryption. If an agent attempts to access the document, it processes only opaque ciphertext. Trellix encryption technology holds FIPS 140-2 validation and complies with standards such as HIPAA, PCI DSS, and GDPR.
Integration Architecture: Kriptos + Trellix
Trellix Helix: Centralization and Noise Reduction in the SOC
Processing three independent exit flows can cause alert fatigue for security analysts. Trellix Helix sits above the channels as a security operations and AI correlation layer, connecting events across traditional DLP, Shadow AI interactions, and autonomous agent activity.
By correlating alerts that reference the same file labeled by Kriptos, false positives are eliminated, providing analysts with a unified, prioritized triage queue.
One Classification Input to Power Your Security Stack
The integration between Kriptos and Trellix demonstrates that automated classification should not be viewed as a standalone product, but as the foundational intelligence layer that powers existing security controls.
Through capabilities like DSPM technology, data access governance, and insider threat management, Kriptos provides Trellix operational tools with the contextual visibility required to protect information on local endpoints and cloud collaboration environments such as Microsoft 365 and Google Workspace.
Strengthen Your Cybersecurity Investment and Protect Your Data Across All Channels
Deploying advanced security tools is insufficient if systems operate blindly on your organization's document estate. Combining Kriptos automated AI classification with Trellix multichannel enforcement delivers the visibility IT teams need to mitigate risks across endpoints, AI tools, and automated workflows.
Streamline your security architecture by labeling files once and allowing your cybersecurity tools to enforce the appropriate controls on every channel. Automatically and continuously reduce your data leak exposure without slowing down employee productivity.
Request a Personalized Kriptos Demo
Discover how to ensure secure AI adoption and protect your company's critical information.
Frequently Asked Questions (FAQ) on Kriptos + Trellix Integration
Why do traditional DLP tools fail to detect most confidential files?
Because 72% of corporate documents do not contain standardized patterns like credit card or national ID numbers. Rule-based traditional solutions fail to interpret the business context of presentations, contracts, or source code unless preceded by a sensitivity label.
How does this solution protect against uncontrolled Artificial Intelligence (Shadow AI)?
Kriptos identifies sensitive documents, while Trellix monitors data movements (clipboard, copy/paste, and file uploads) across more than 400 AI applications, preventing confidential information from being shared on public platforms.
Is it necessary to replace existing cybersecurity infrastructure?
No. Kriptos integrates seamlessly with your current security ecosystem (including Trellix DLP, encryption, and SIEM/Helix), acting as the intelligence layer feeding your installed operational controls.
References and Sources
- IBM Security, Cost of a Data Breach Report 2025 — Incidents involving Shadow AI added an average of $670,000 USD to breach costs; 97% of AI-breached companies lacked access controls.
- Accenture, State of Cybersecurity Resilience 2025 — Only 20% of organizations feel confident in their ability to secure generative AI.
- Trellix, DLP Endpoint, Data Encryption, and DLP AI Data Risk Dashboard Data Sheets (Musarubra US LLC, 2024–2026).
- Kriptos Benchmark, Aggregated data analysis across 1.2B+ classified corporate documents.


